Quick Take
- Cursor identified malicious Claude Code extension versions 2.1.312 and 2.1.313 for macOS and Windows in its marketplace.
- Uninstalling may leave persistence behind, while successful remote access depended on SSH configuration and host permissions.
- Cursor recommends host cleanup and rotating accessible credentials and sessions from a trusted system; crypto theft is not established.

Code editor Cursor is urging developers who installed malicious Claude Code extension packages from its marketplace to clean affected machines and rotate accessible credentials and sessions from a trusted system. Removing the extension alone may leave persistent components running, the company warns.
The affected packages are Anthropic.claude-code versions 2.1.312 and 2.1.313 for macOS and Windows. Cursor’s security notice places their availability between about 2:27 a.m. and 1:35 p.m. PT on Oct. 29, 2026. Cursor says Anthropic did not develop the malicious versions and reports no evidence that other versions or the official distribution were affected.
Cursor clarified the affected versions and indicators on Oct. 30. Security researcher Phorion updated its malware analysis on Oct. 31 to include both versions, having initially identified only 2.1.313.
Why uninstalling may leave access behind
According to Phorion, the payload attempts to add an attacker-controlled SSH key, enable the machine’s SSH remote-login service and establish a reverse tunnel. With SSH running, the planted key could let an attacker log in through that tunnel. Persistence mechanisms include a macOS LaunchAgent and, on Windows, an attempted scheduled task with a Startup-folder fallback.
Phorion says the injected code executes when Node loads the extension module, before its normal activation callback. No further interaction with the extension is required at that point.
Successful remote access also depended on the host. Phorion found that a permission-check bug causes the macOS code to skip enabling Remote Login when run as a standard user. If SSH was already enabled, or enabled later, the planted key could still permit access while the tunnel was operational.
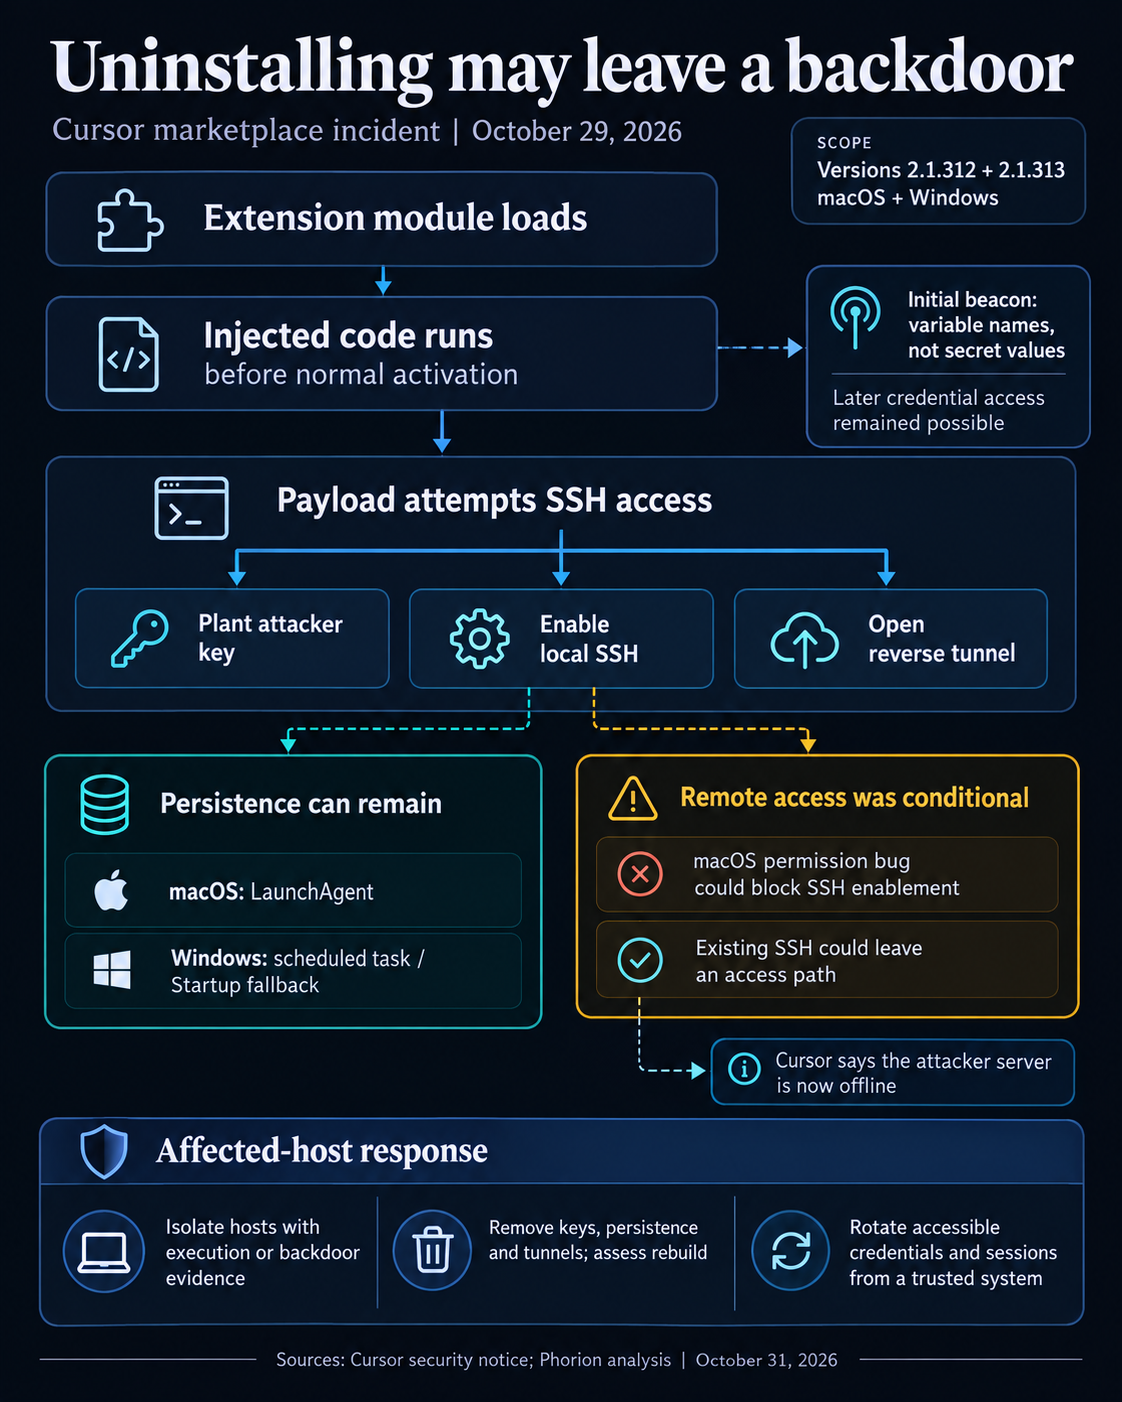
Cursor says it worked with the hosting provider to take the attacker server offline. It also removed the packages, rotated its keys and rebuilt and reopened the marketplace. Those steps do not remove components already left on an affected machine.
The initial beacon reported host information and up to 40 matching environment-variable names, rather than their secret values, according to Phorion. Cursor cautions that this limited collection does not rule out later credential access through the backdoor.
For crypto developers, Cursor’s advice would extend to development or financial-service credentials accessible to the affected local user account, if present. Neither advisory establishes cryptocurrency theft or crypto-specific targeting.
Cursor recommends checking endpoint, network and extension-installation records, isolating hosts showing payload execution or backdoor installation, and removing unauthorized SSH keys, persistence mechanisms and running tunnels. Its notice provides platform-specific remediation scripts and advises assessing whether the host should be rebuilt.
Cursor also recommends rotating credentials and sessions accessible from affected hosts using a trusted system.
Mentioned in this article
Editorial credits