
Quick Take
- 71% of Bitcoin Lightning nodes flagged in an August security disclosure remained on affected software lines in October.
- Fixes had been available for more than a year, exposing persistent delays in securing Bitcoin's payment infrastructure.
- Security warnings failed to trigger a measurable acceleration in upgrades, raising questions about how operators can be pushed to patch.


Nearly three-quarters of public Bitcoin Lightning nodes identified as exposed in August remained on affected software lines in October.
An Oct. 21 study found that 71% of a group of 550 public LND nodes flagged during an Aug. 11 security disclosure were still operating on affected software release lines as of Oct. 13.
Only about 10% had upgraded during that period, while 108 nodes were no longer classified as live. The findings suggest that security fixes are reaching some Lightning operators well after their release dates.
The delays are particularly striking because patches for six vulnerabilities covered by the August disclosures had been available since LND version 0.19.0, released 446 days before the public warning.
LND is one of the software implementations used to operate nodes on Bitcoin's Lightning Network, which processes payments outside the blockchain's main transaction layer.
Lightning upgrades follow platform releases rather than security warnings
Research by Saurabh Kumar of Bitcoin Data Labs found that the network's largest software upgrade waves closely followed releases from Umbrel, a platform that packages Bitcoin node software.
The three biggest waves involved between 262 and 385 nodes each, with at least 87% of participating nodes broadcasting updated software features within 48 hours of an Umbrel release.
However, Umbrel distributed those versions between 19 and 41 days after the corresponding LND releases, introducing another potential delay between developers making fixes available and operators receiving them through their preferred platforms.
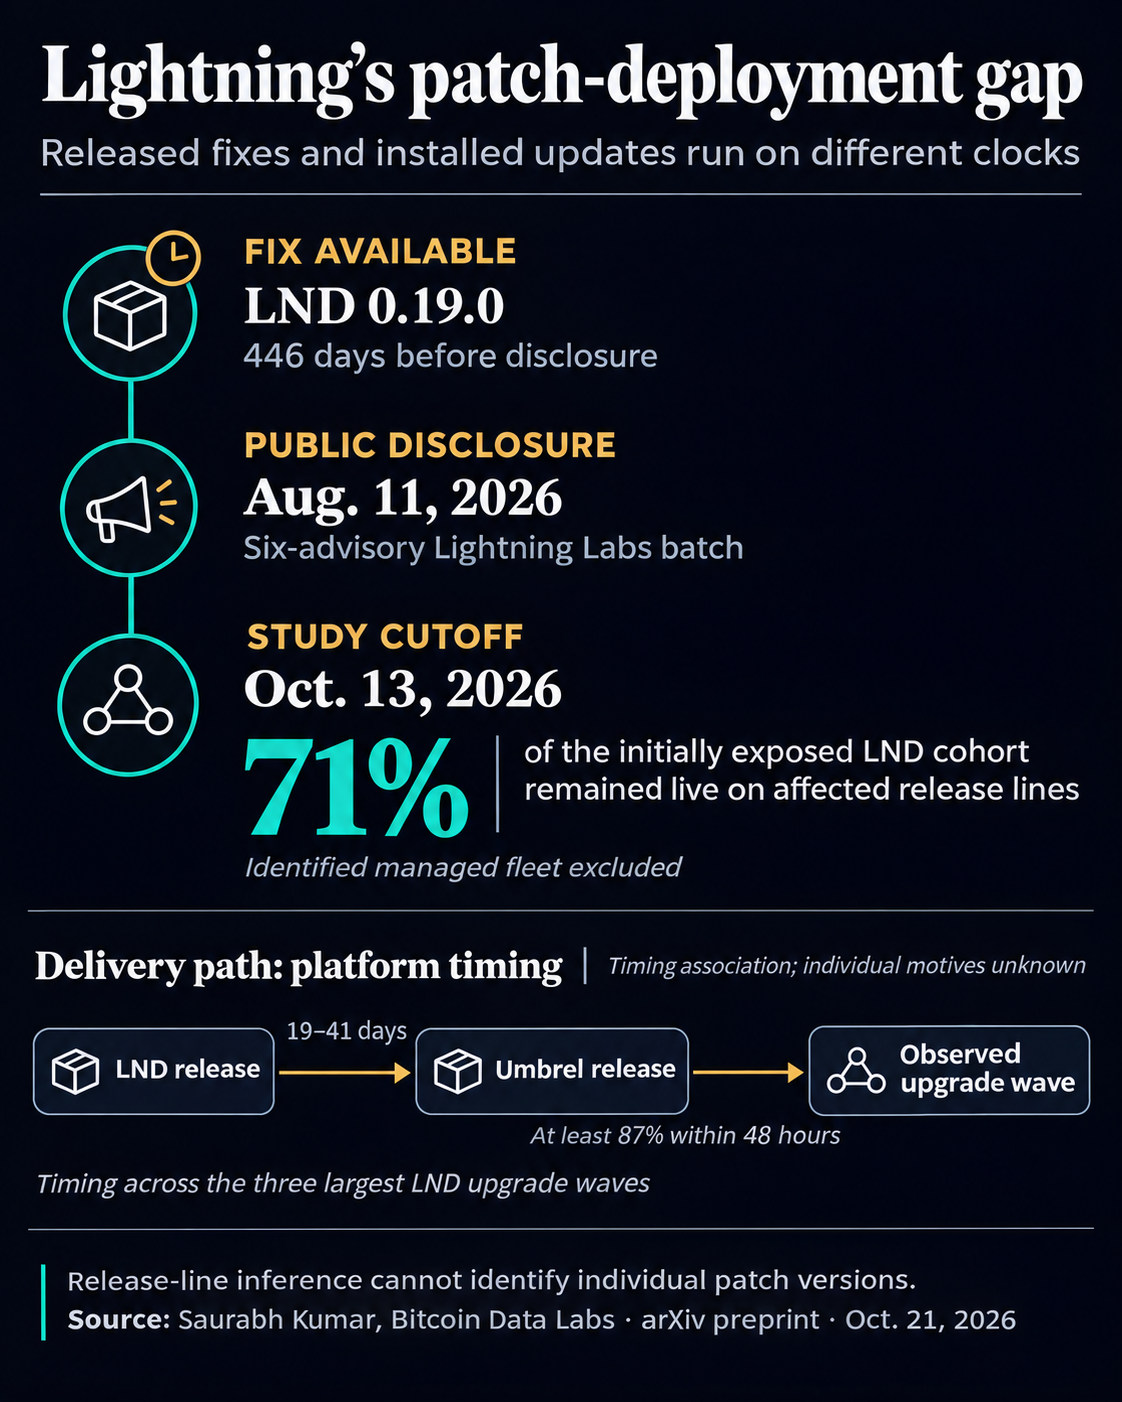
The association suggests that software distribution channels can significantly influence how quickly Bitcoin's payment infrastructure adopts security improvements. The study could not identify which platforms individual nodes used, leaving the precise role of automatic updates unresolved.
Public security warnings appeared less effective at changing operator behavior.
Across nine LND vulnerability disclosures, the researcher found no statistically detectable acceleration in nodes moving away from affected software lines. The findings do not rule out smaller responses, but they show that disclosures were not followed by clear, widespread upgrade surges.
The delays also extend beyond security incidents. Nodes operating older software when LND versions 0.19 through 0.21 became available took an estimated median of 88 days to migrate to the newer release lines.
Still, the potential exposure is unevenly distributed across Lightning's payment infrastructure.
At the August disclosure, affected release lines accounted for 14.9% of live LND nodes but only 6.4% of their channel capacity, excluding an identified managed fleet. That disparity suggests that affected nodes controlled a relatively smaller share of payment liquidity.
The researcher analyzed 814 daily snapshots of Lightning's public network graph, using advertised software features to infer release lines. The method cannot identify exact patch versions, and nodes that upgrade without broadcasting new announcements may continue to appear exposed. Actual exploitability also depends on the vulnerability and the node's configuration.
Kumar published the study's code and aggregate data alongside the preprint, allowing further scrutiny of the findings. The research leaves node software developers and platform distributors facing an unresolved operational question: how to reduce the weeks or months between releasing security fixes and getting them installed across Lightning's public network.
Mentioned in this article

Editorial credits