Quick Take
- Binance says it removed all SignalPlus-linked API keys and told affected users to review positions and open orders directly.
- Deribit said connected-key revocation stopped trading, monitoring and automation through SignalPlus, while users could check accounts directly.
- SignalPlus reported losses below $82,000, said reimbursement had begun and pledged to repay all affected users in full.


Binance cut its connections with crypto trading platform SignalPlus on Nov. 5 after a security warning. SignalPlus later said attackers had broken into its network after an engineer was tricked with a fake Microsoft Teams meeting invitation.
API keys let software access an exchange account within the permissions a user grants. In its advisory, Binance described the revocation as an immediate precaution and said its own systems were unaffected and user funds remained safe.
Deribit later issued its own notice. Deribit said it had revoked all customer API keys connected to SignalPlus, stopping trading, monitoring and automation through that connection. It said Deribit's systems and data were unaffected, and directed users to check their accounts on Deribit itself.
SignalPlus subsequently described an attack it had detected in the early hours of Nov. 4. In a statement, SignalPlus put losses below $82,000 in its assessment to date and said it had begun reimbursing affected users.
Binance told SignalPlus users to check both positions and open orders through its own platform. Binance recommended waiting until SignalPlus confirms full resolution before reconnecting API keys, and enabling IP whitelisting.
Deribit's guidance covered open orders, positions and recent account activity. @DeribitOfficial also recommended IP allowlisting and waiting for official communication from SignalPlus before reconnecting. Its notice described the interruption to functions through SignalPlus, while directing users to manage their accounts through the exchange.
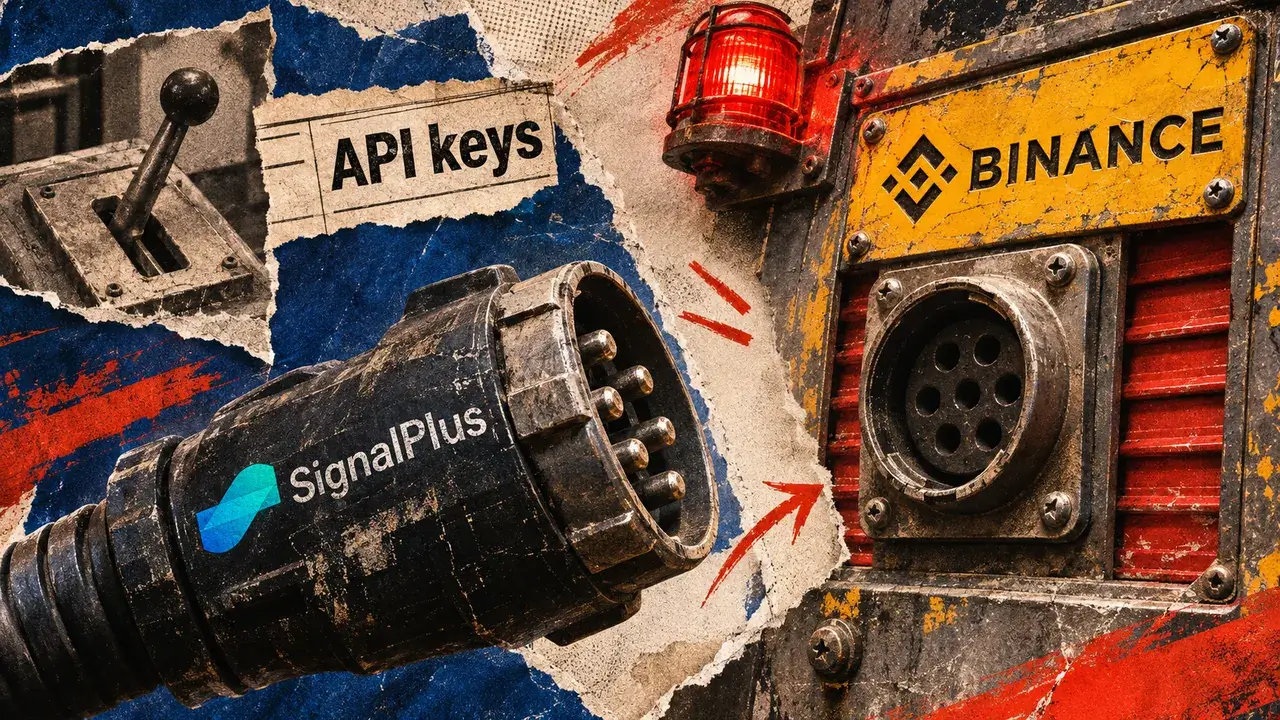
SignalPlus keys revoked. Check accounts directly.
Binance and Deribit say they revoked SignalPlus-linked API keys and directed users to review their accounts on the exchanges themselves.
Check positions and open orders directly on the exchange, and wait for SignalPlus communication before reconnecting.
Reported exchange actions and guidance, not independent proof of account safety. The diagram does not show specific user permissions, order execution status or a completed SignalPlus recovery.
Sources and evidence
Sources
Supporting facts
- @binance said on Nov. 5 that it proactively removed all API keys linked to SignalPlus as an immediate precaution after SignalPlus reported a potential security issue. [1]
- Reported statement @binance told SignalPlus users to log in to Binance directly to review positions and open orders, wait for SignalPlus to confirm full resolution before rebinding API keys, and enable IP whitelisting. [1]
- @DeribitOfficial said it proactively revoked all customer API keys connected to SignalPlus after SignalPlus raised a potential security concern, and said Deribit systems and data were unaffected. [2]
- Reported statement @DeribitOfficial said trading, monitoring and automation through SignalPlus had stopped, and directed users to check open orders, positions and recent account activity directly on Deribit. [2]
- Reported statement @DeribitOfficial advised users to enable IP allowlisting and wait for official communication from SignalPlus before reconnecting. [2]
Method
A qualitative access-route diagram using the Nov. 5 Binance and Deribit notices. Connectors show account access, not transactions or fund movements. No numerical scaling or inferred permissions.
Scope
Reported exchange actions and guidance, not independent proof of account safety. The diagram does not show specific user permissions, order execution status or a completed SignalPlus recovery.
 CryptoSlate
The advice extended beyond those two exchanges. In a post responding to Binance's advisory, Changpeng Zhao urged people using SignalPlus on other exchange platforms to revoke their API keys and advised against storing keys with third-party platforms.
Binance also called on third-party platforms integrated with it to review their security controls, monitor unusual activity and contact the exchange immediately if they detected concerns.
How the SignalPlus attack reached exchange API keys
SignalPlus said its investigation traced the incident to a compromised Telegram account belonging to a contact at a third-party technology vendor. According to the company, the attacker impersonated that contact and sent an engineer a fake Microsoft Teams meeting invitation that compromised the engineer's computer.
SignalPlus said it detected the attack in the early hours of Nov. 4 and contained the intrusion. SignalPlus said it contacted partner exchanges to disable every user API key associated with its platform and suspended services for a comprehensive security review.
The company said full reimbursement had begun on a case-by-case basis and pledged to repay all affected users.
Binance's Spot API documentation separates permission to place and cancel orders from permission to view private account information, such as order status and trading history. Trading permission must be enabled explicitly. Binance gives the example of one key for trading and another for monitoring order status.
IP allowlisting adds a separate restriction. Binance Academy's guidance explains that, when IP restrictions are enabled, requests from addresses outside the key's whitelist are rejected.
SignalPlus acknowledged that it had not previously made IP whitelisting mandatory for exchange API access. It said it would tighten API access requirements and strengthen endpoint security, internal access controls and key management as part of its response.
SignalPlus said services would return in phases after its review, necessary patches and confirmation that restoration was safe. Its statement supplied no fixed reopening date.
Mentioned in this article

Editorial credits