Quick Take
- CoinDCX says failed sweeping of deposits from deprecated wallets caused losses it absorbed, while affected customers were credited.
- ZachXBT alleges $15.8 million in user deposits went unaccounted for, a figure CoinDCX did not quantify in its update.
- A confirmed 15,819,002 USDT transfer establishes token movement, but does not prove wallet control or customer losses.

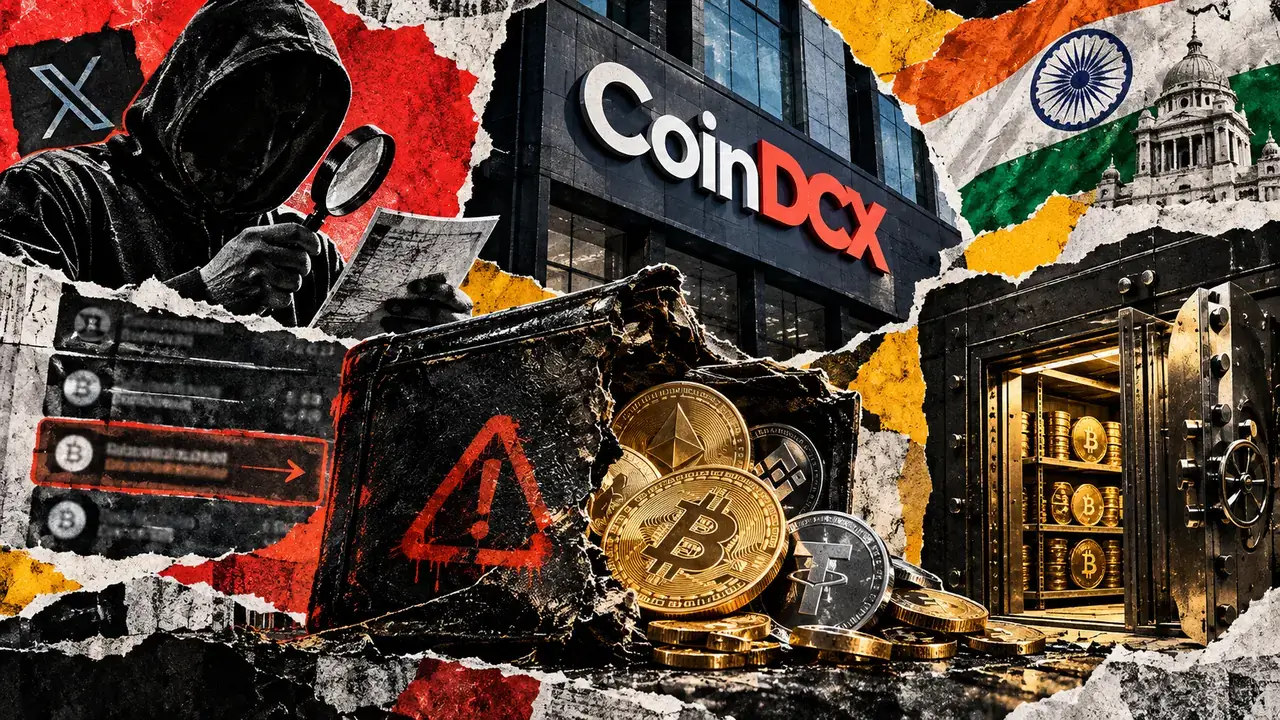
Indian crypto exchange CoinDCX said it absorbed operational losses after a process for collecting deposits from old wallet addresses failed, adding a new explanation on Oct. 22, hours after denying a fresh breach.
In a 12:47 p.m. BST update from CoinDCX, the exchange said some users had continued sending crypto to addresses deprecated after its July 2025 security incident. It said it credited affected customer deposit wallets, while active wallets remained unaffected.
The statement followed an allegation by ZachXBT that $15.8 million in user deposits was unaccounted for. CoinDCX did not give a loss amount in its update or specify how long the failed process had lasted.
According to CoinDCX, the company had retired the addresses from use, but some users kept depositing despite earlier warnings.
Its sweeping process was supposed to regularly collect those deposits so the company could account for and secure them, but it only discovered the failure on the morning of Oct. 22.
From denial to an explanation of losses
At 9:10 a.m. BST, CEO Sumit Gupta said CoinDCX wallets had not been breached. He described the flagged addresses as created in January 2025 and compromised in the July 2025 incident. He also said none of CoinDCX's current central or user addresses had sent money to them.
Four minutes later, CoinDCX said the exchange hadn't used those old addresses since July 2025 and that the reported activity had no connection to CoinDCX. At 9:38 a.m. BST, the account pointed readers to Gupta's denial.
At 9:52 a.m. BST, ZachXBT challenged that account. He alleged the deposit address TQKJQ remained in use after the July 2025 incident, describing its use as lasting “for 10 months” after that incident.
He also alleged the address swept user deposits to CoinDCX's current public hot wallet and received transaction-fee funding.
At 10:59 a.m. BST, Gupta replied that he was aware of the claim, that it was being investigated further, and that no user funds would be lost.
TronGrid event data and TronScan's transaction record reviewed by CryptoSlate show a single successful transfer of 15,819,002 USDT from the address beginning TQKJQ to another TRON address at 4:35:54 p.m. BST on Oct. 21.
The transfer confirms the tokens moved, but it doesn't show who controlled either address or whether customers lost funds.
In its later update, CoinDCX maintained that customer assets were held in segregated cold wallets and that trading continued normally.
The old addresses relate to the July 2025 incident. Security firm Cyvers linked a roughly $44 million incident to the Lazarus Group, and CoinDCX said its treasury covered the loss. On July 31, Gupta's preliminary explanation pointed to social engineering.
The unresolved accounting issue is how much CoinDCX absorbed and when the sweep failed. Its Oct. 22 update acknowledges those operational losses while leaving both details unspecified.
Mentioned in this article

Editorial credits